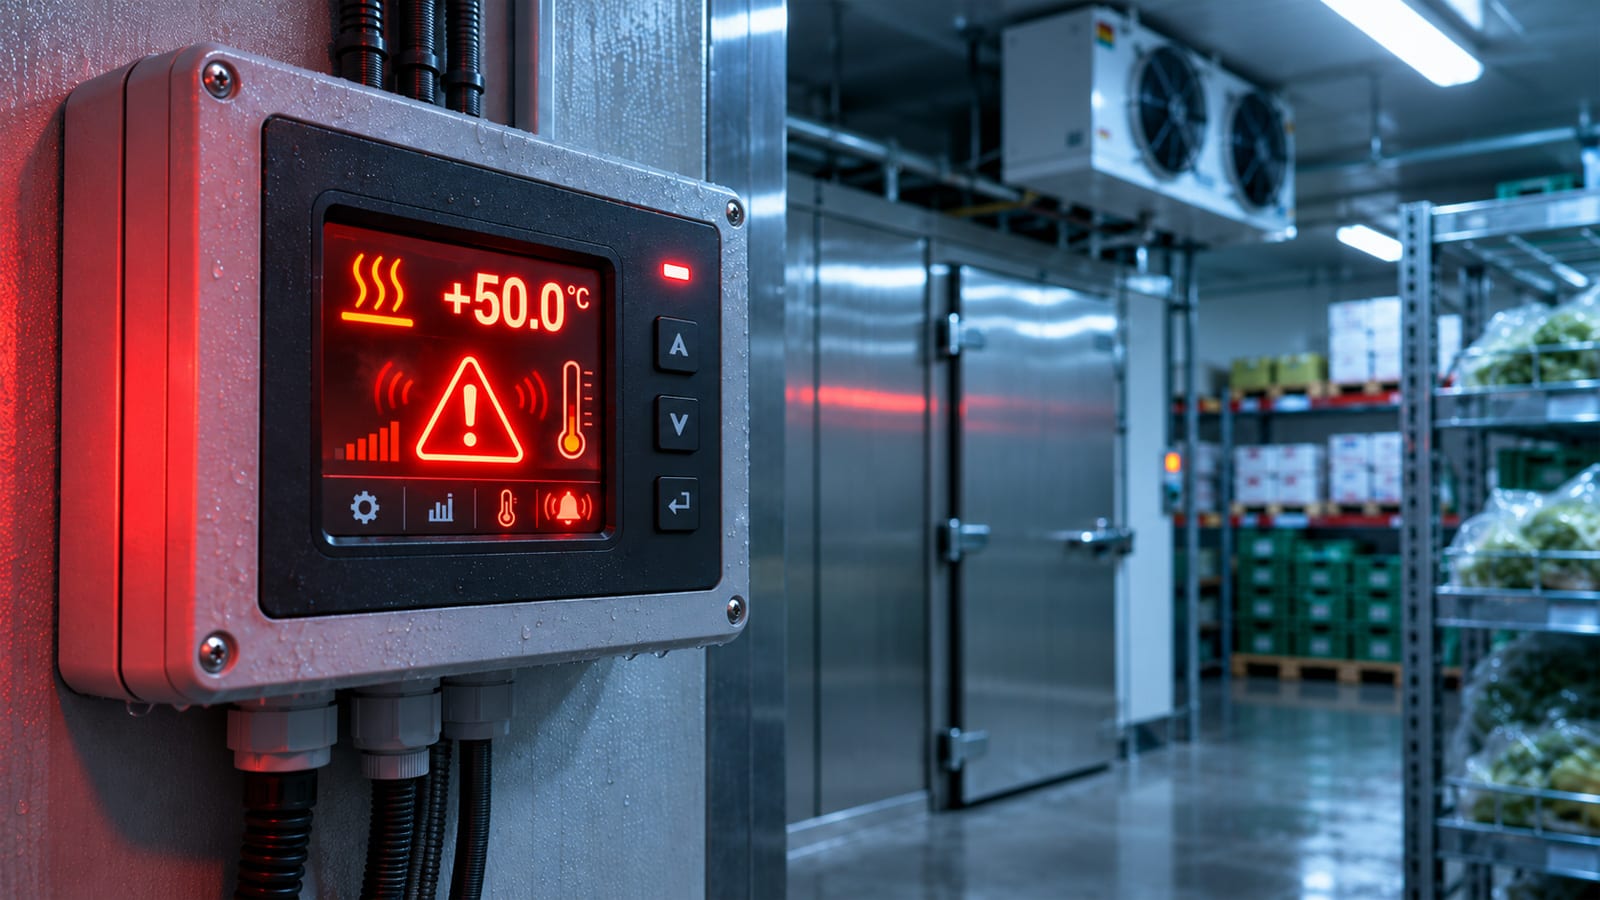
Act this weekWhat happenedThe FBI, CISA and other US agencies warned that hackers are actively attacking refrigeration controllers, changing temperatures and forcing equipment into heating or defrost modes.
Who is affectedGrocery stores, cold storage sites, food producers, healthcare facilities, chemical facilities and transportation firms that use internet-connected temperature controllers.
What to do- 1Take refrigeration controllers off the public internet.
- 2Secure any remote access you need and change default passwords.
- 3Install the latest security updates from your equipment maker.
- 4Keep cooling systems separate from office networks and set safe temperature limits.
US agencies are warning that hackers are actively breaking into the controls that run commercial freezers and coolers. The FBI and CISA, the federal cyber defense agency, say attackers are changing temperature settings, which can spoil food, damage equipment and even start fires. The warning also came from the health, agriculture and transportation departments.
What happened
The agencies say attackers are going after electronic temperature controllers and refrigeration management systems that are out of date or reachable from the internet. These devices let staff check temperatures remotely, manage defrost cycles and control cooling equipment.
Hackers can bypass logins, inject their own code or take advantage of weak settings. Then they can force equipment into nonstop heating or defrost cycles. They may also hide the real temperatures, so staff do not notice a problem until it is too late.
Where it has already happened
The US warning follows attacks in Europe. In October, hackers got into refrigeration controllers at an estimated 250 to 350 French supermarkets. They switched on defrost functions and raised temperatures in fridges and freezers.
A second wave in November hit more than 115 stores in six European countries. Some systems shut down entirely. Others heated up to 50°C (122°F). On November 3, the French Blood Establishment confirmed that an incident at a refrigeration equipment provider changed temperature and defrost settings at three sites that store blood products.
Who it affects
The agencies point to grocery stores, cold storage sites, food producers, healthcare facilities, chemical facilities and transportation firms. A restaurant or small shop with remote-access cooling controls could be exposed too. CISA's Chris Butera said every organization that depends on these systems should assume it could be a target.
Who can relax a little? The warning is about commercial and industrial equipment. Home refrigerators are not mentioned. Businesses whose controllers cannot be reached from the internet and are fully updated face less of the risk the agencies describe.
What to do
The steps are in the alert box above. The first move is simple to ask about: find out whether your cooling controls can be reached online, and call your equipment vendor or service company to ask about security updates.
What happens next
The agencies call the threat ongoing. The material does not say who is behind the attacks or how many US sites, if any, have been hit. Expect more guidance from equipment makers, and watch for news from your own vendor.
The takeawayIf your business runs cooling controls that can be reached online, ask your vendor today about updates and take them off the public internet.