Act this weekWhat happenedEnergize Lab confirmed security problems in its Eiliko AI robot charm, but The Verge found photos and audio still exposed after the company said access was closed.
Who is affectedOwners of the Eiliko robot charm, including anyone whose voice, face or chats the toy captured.
What to do- 1Stop using the Eiliko toy and app until the security review is finished.
- 2Do not share personal details, photos or private talk with it.
- 3Remove the app and any custom avatar photos you uploaded.
- 4Email security@energizelab.com to ask that your stored data be deleted.
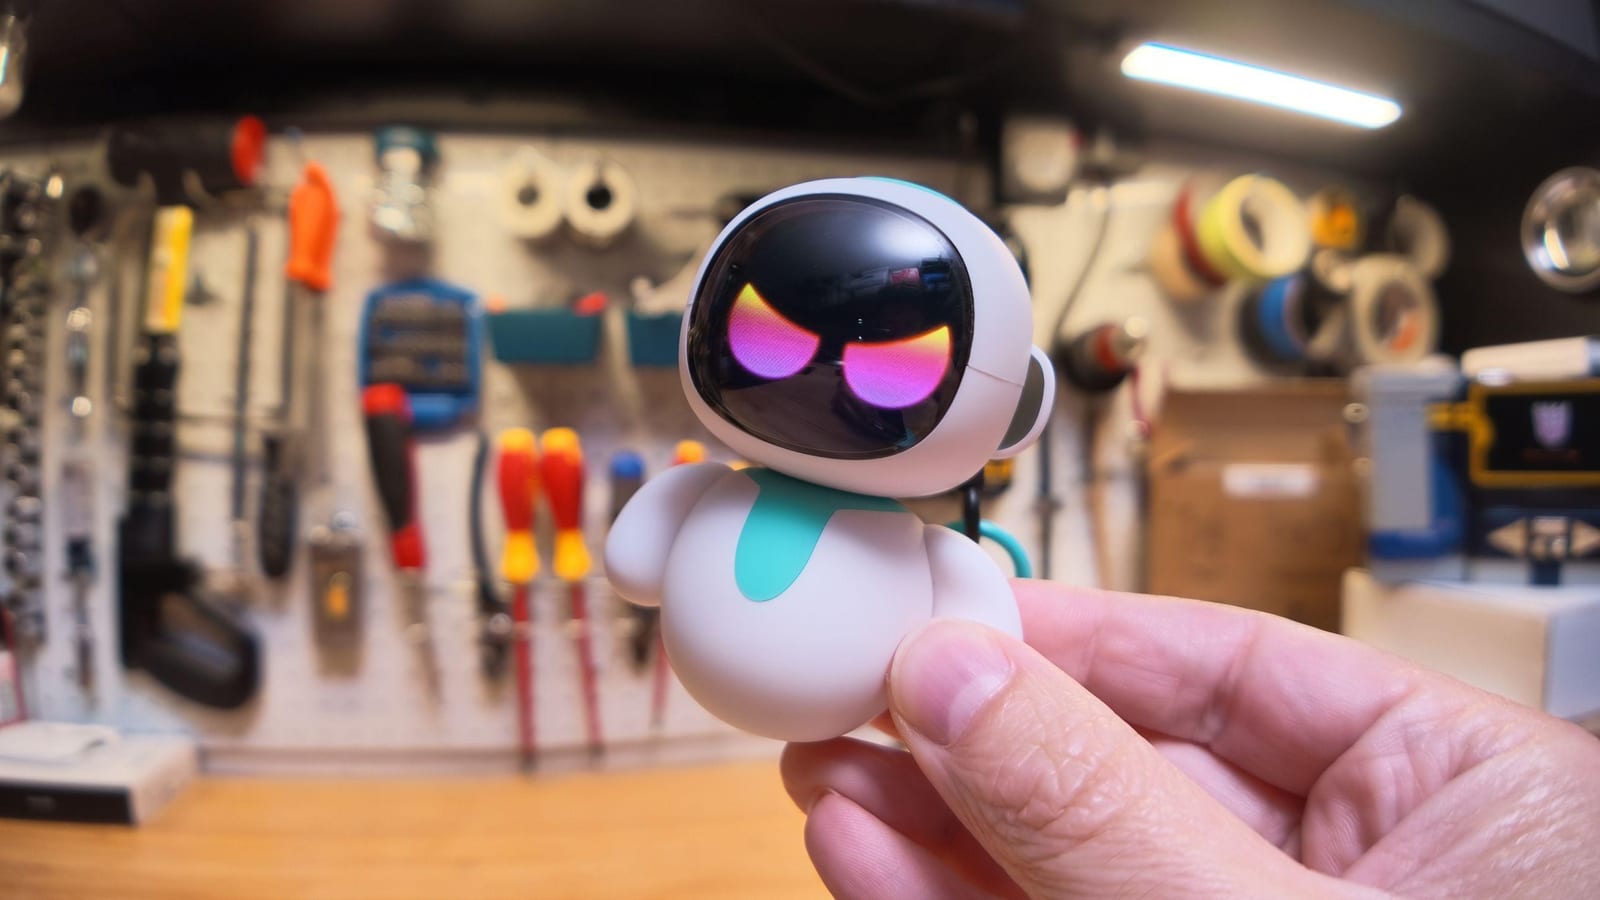
The company behind Eiliko, a small AI robot charm that hangs on a bag, has admitted its toy had serious security problems. But The Verge reports that some problems were still open after the company said they were fixed. Photos and audio of owners were still sitting on public web links.
What happened
Eiliko holds AI conversations with its owner. It told owners that "your secrets are safe with me." The Verge and security researcher Sammy Azdoufal found that hackers could easily read complete transcripts of everything said to the toy. They spent over a month trying to reach the maker, Energize Lab, including emails to CEO and founder Shaw Yeung. Nobody answered until now.
What the company says
Energize Lab sent an unsigned statement from a generic email address. It later said the statement comes from CTO Du Xiaoyu. The company says it has confirmed the core issues and has done the following:
- Closed all outside access to its backend systems and changed its access credentials.
- Turned off the feature that let a robot's responses be changed remotely.
- Taken long-term memory offline and stopped storing conversation records and user profiles.
- Taken custom avatars offline. The app now offers built-in avatars only.
It also promises to delete stored conversations, profiles and avatar images, and to hire an independent security firm to review all its systems.
What is still not fixed
With Azdoufal's help, The Verge confirmed that as of the company's email, audio recordings and photos were still stored at public web addresses with no protection. The reporter says a click on the right link would show an owner's face. The link was not shared. Azdoufal also says he still has full SSH access to the robots, meaning a way to log in from afar. He says he can in theory still read transcripts and change the toy's behavior. That does not match the claim that all outside access is closed.
Who is affected
Owners of the Eiliko robot charm are affected, along with anyone whose voice, face or chats the toy captured. That can include family members and children who talked to it. The company says memory and custom avatars will not return until the review confirms they are secure. That wording suggests it still plans to store some personal information later. The alert box above lists the steps to take.
What happens next
Energize Lab says it will share an update once the independent review is done. It has not said when that will be, or which firm will do the work. It also has not shown that the stored photos, audio and chats have actually been deleted. In its words, it intends to earn back trust "through what we do in the coming weeks." Until outside checks show the exposed links are closed, the company's claims are not proven.
The takeawayTreat the Eiliko toy as unsafe for now: its maker admits flaws, and exposed photos and audio were still online after it said access was closed.