Act todayWhat happenedResearchers found a rentable Android spyware kit, uCreator, that hides in altered copies of Telegram and WeChat to steal passwords and clone accounts.
Who is affectedAndroid users of Telegram and WeChat who install apps from outside official stores or run WeChat inside the kit's own container app.
What to do- 1Install Telegram and WeChat only from Google Play or the makers' official sites.
- 2Do not install app files sent by links, ads or chat messages.
- 3Check the device list in your Telegram settings and end any session you do not know.
- 4If you installed a copy from elsewhere, delete it and change your passwords from a clean device.
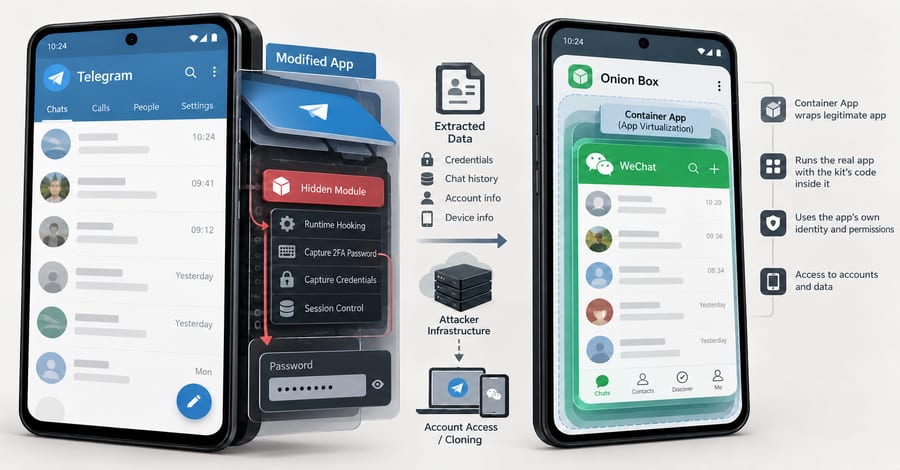
Researchers have described an Android spyware kit, called uCreator, that is rented out to criminals and hides inside working copies of Telegram and WeChat. The altered apps look and behave like the real ones. In the background, they can copy a Telegram password, read chats and help attackers take over the account.
What happened
Researcher Ovi published the analysis on October 21, 2026. The kit adds its own code to a real app, so the spyware runs with the same access as the signed-in app. In Telegram, it can copy the two-step verification password, an extra password some people set, before the app scrambles it. With it, attackers can log other devices out, change the linked phone number or delete the account.
The kit can also hide the attacker's login from the device list shown inside the altered app. That makes a takeover harder to spot. For WeChat, the kit can copy out the account's login identity and use it to clone the account.
Who it affects
Only people who install one of the altered copies are exposed. These spread by sideloading, which means installing an app file directly instead of from an app store, and through social engineering, meaning tricks that persuade people to install. The kit makers also run a container app called Onion Box, which runs other apps inside itself. WeChat run there can be targeted too.
A matching Telegram campaign is known. Doctor Web reported a backdoor called Baohuo in October 2025 and estimated more than 58,000 infected devices. Its code, server and command names match the kit. It is not clear who ran that campaign. Some fake copies even use the same package name as the real app on Google Play, so the name alone proves nothing.
Who can relax
If you only install Telegram and WeChat from official sources, this does not reach you. Ovi also calls his report an analysis of what the kit can do, not a measure of how many victims there are. He says it does not prove attackers have used every step from start to finish.
What to do
The alert box above lists the steps. The short version: stick to official sources, skip app files sent through links, ads or chats, and check your Telegram device list for sessions you do not know.
What is not known yet
Ovi found code supporting about 20 apps but has published code only for Telegram and WeChat. Other possible targets, such as WhatsApp, LINE and GCash, are unconfirmed. Ovi could not confirm how every victim was infected.
It is also unclear whether a hidden session would show on a person's other, untampered Telegram apps. Neither Ovi nor Doctor Web gives steps for securing an account taken over this way. The kit's hooking tool had trouble on a Pixel 10 Pro running Android 17. Ovi says that is extra work for its makers, not proof that Android 17 blocks the attack.
The takeawayInstall Telegram and WeChat only from Google Play or the official sites, and check your Telegram device list for sessions you do not recognize.